I pulled off my first phishing campaign at 14 years old; at the time, I didn’t even know it was called phishing. Despite that, I have never considered myself to be a “good” hacker, just a mere script kiddie. Classical hacking was always too boring to me, and I spent my time working for stable pay rather than hunting bug bounties. But something has changed. I placed 3rd in CESNET’s ongoing competition, The Catch. A single agent running stock DeepSeek V4.1 Flash did this with minimal help from my side. GLM-5.3 had to be summoned for just one task. And there were no effective guardrails, nothing stopping me. Chinese models don’t care (mostly). It took exactly $2.98 worth of credits per official pricing…
Besides that, my agents “hacked” a dozen systems over the last two months, sometimes without being asked to do so. They accessed restricted materials on a state geology portal, bypassed reCAPTCHA while scraping thousands of entries from another agency’s portal, downloaded thousands of high-value images from some company’s unprotected Azure Blob storage, and pulled some solid reverse-engineering work. And some of these were done just by a little local Qwen 3.8-27B, quantized up to the point the guys from r/localLLM would call “braindead”.
Do you want to learn more about how to jailbreak stock Chinese (or OpenAI) models easily? I will post a write-up about The Catch shortly. Stay tuned!
Now imagine what the gentlemen with unrestricted access to the latest Mythos (or even better, undisclosed models) are pulling off daily. I’ve heard some wild stories over there, but we can also see what is happening in the open. The number of disclosed CVEs is exploding. Canonical is (finally) transitioning to weekly security updates for their kernel fork. October 21st was one of the worst “breachocalypse” ever… And I am just wondering what the grey market with exploits, on which many companies like InvaSys and NSO Group rely, looks like.
I would argue that with all these tools available, after the “breachocalypse” we’re witnessing these weeks, the number of exploitable vulnerabilities in new SW and HW will inevitably converge to zero. Of course, the “tail vulnerabilities” will live for much longer – there are many companies (and even more so, state agencies) that are still asleep. Have you ever seen, for example, the UI used by the employees at the Czech Post? Or what the ladies in the tax offices use? Strict network isolation is the only thing protecting us from the absolute catastrophe there. But these legacy systems will die someday too.
Anyway, the fact is that classical hacking is dead. But hackers (either white hat or black hat) won’t go away. The “think-out-of-the-box” skill is not something that you can just throw away, just like the telephone switchboard operators when replaced by automated systems. Hackers (at least the best ones) will find their way to show that skill. But where will their focus shift?
The obvious path would be enhancing social engineering attacks, finding novel ways of prompt injections, or fine-tuning open models into bad, sleeper ones, or protecting against them. But that knowledge would be obsolete fast, due to the same mechanism in play – better and better AI models.
Did you try it physically?
For a long time, I had hoped that the focus of many companies, when it comes to security, would drift from the purely virtual world of code, hot data, and… maybe some social engineering, into the physical world. Why? Because pentesting web apps is boring. Making phishing campaigns? Boring. But breaking into buildings, on the other hand, is a good source of fun and adrenaline.
However, over the years, physical pentest jobs were scarce. And the reasons are simple. Especially here in Central Europe:
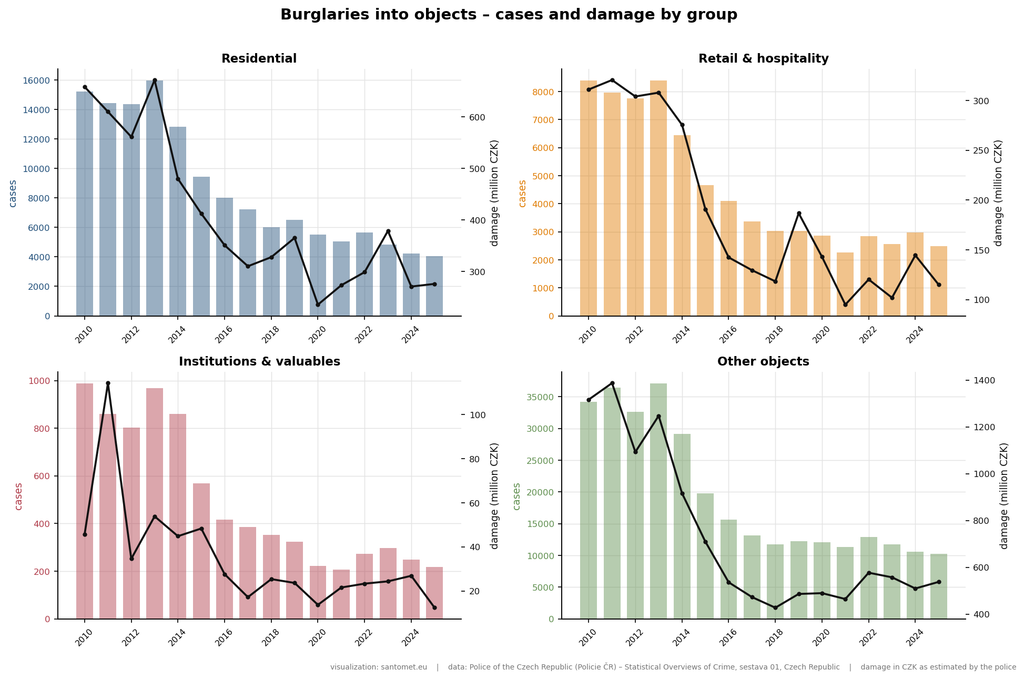
- The number of burglaries and damages caused by these has been dropping. However, it has been quite stable in the last few years…
- If someone wanted a physical pentest, it was typically a state institution or a subject with critical infrastructure. And we have some government agencies doing this.
- Or, they made a competition (tender), and of course, the one with the best info about other bids… won (And don’t be naive; it is not a local thing. Everywhere in the world it works like that)
This time, it might actually change. After the inevitable horror we’re in right now ends, the best way in will remain the physical way. And don’t be mistaken, AI is already playing a significant role here too – every week, I am vibecoding utilities that were available only to law enforcement until now. And my agents were able to obtain valuable information related to mechanical security that would be hard to get without them, and some of that information has the potential to breach whole buildings.
However, we are still (hopefully) far enough from robots replacing every human activity. Hence, a proper physical engagement will probably need a human behind everything. Maybe I am mistaken, but that is my hope, because I finally want to do the type of redteaming that I enjoy the most. But for that, the demand for physical redteaming must increase so that there are bits of the cake left for independent companies like ours…
What do you think?